TA505
No sourced public emblem in this profile.
reference profile · reported nexus: RU (not nationality)
TA505, the name given by Proofpoint, has been in the cybercrime business for at least four years. This is the group behind the infamous Dridex banking trojan and Locky ransomware, delivered through malicious email campaigns via Necurs botnet. Other malware associated with TA505 include Philadelphia and GlobeImposter ransomware families.
Source-reported aliases: SectorJ04, SectorJ04 Group, GRACEFUL SPIDER, GOLD TAHOE, Dudear, G0092, ATK103, Hive0065, CHIMBORAZO, Spandex Tempest. Associations do not prove equivalence.
Target geography
Catalog-listed countries (associations, not attack counts):  Australia ·
 Canada ·
 Czech Republic ·
 Germany ·
 Hungary ·
 India ·
 Japan ·
 Romania ·
 Serbia ·
 Singapore ·
 South Korea ·
 Spain ·
 Thailand ·
 Türkiye ·
 United Kingdom ·
 United States of America
No bound claim-post feed for this label.
Historical casebook
No dated record curated yet; absence does not establish inactivity.
Planned Kinwilder coverage
Tentative editorial review windows, contingent on evidence and review; not promised publication dates or predictions of attacks.
No assigned review window.
References
https://www.proofpoint.com/sites/default/files/ta505_timeline_final4_0.png
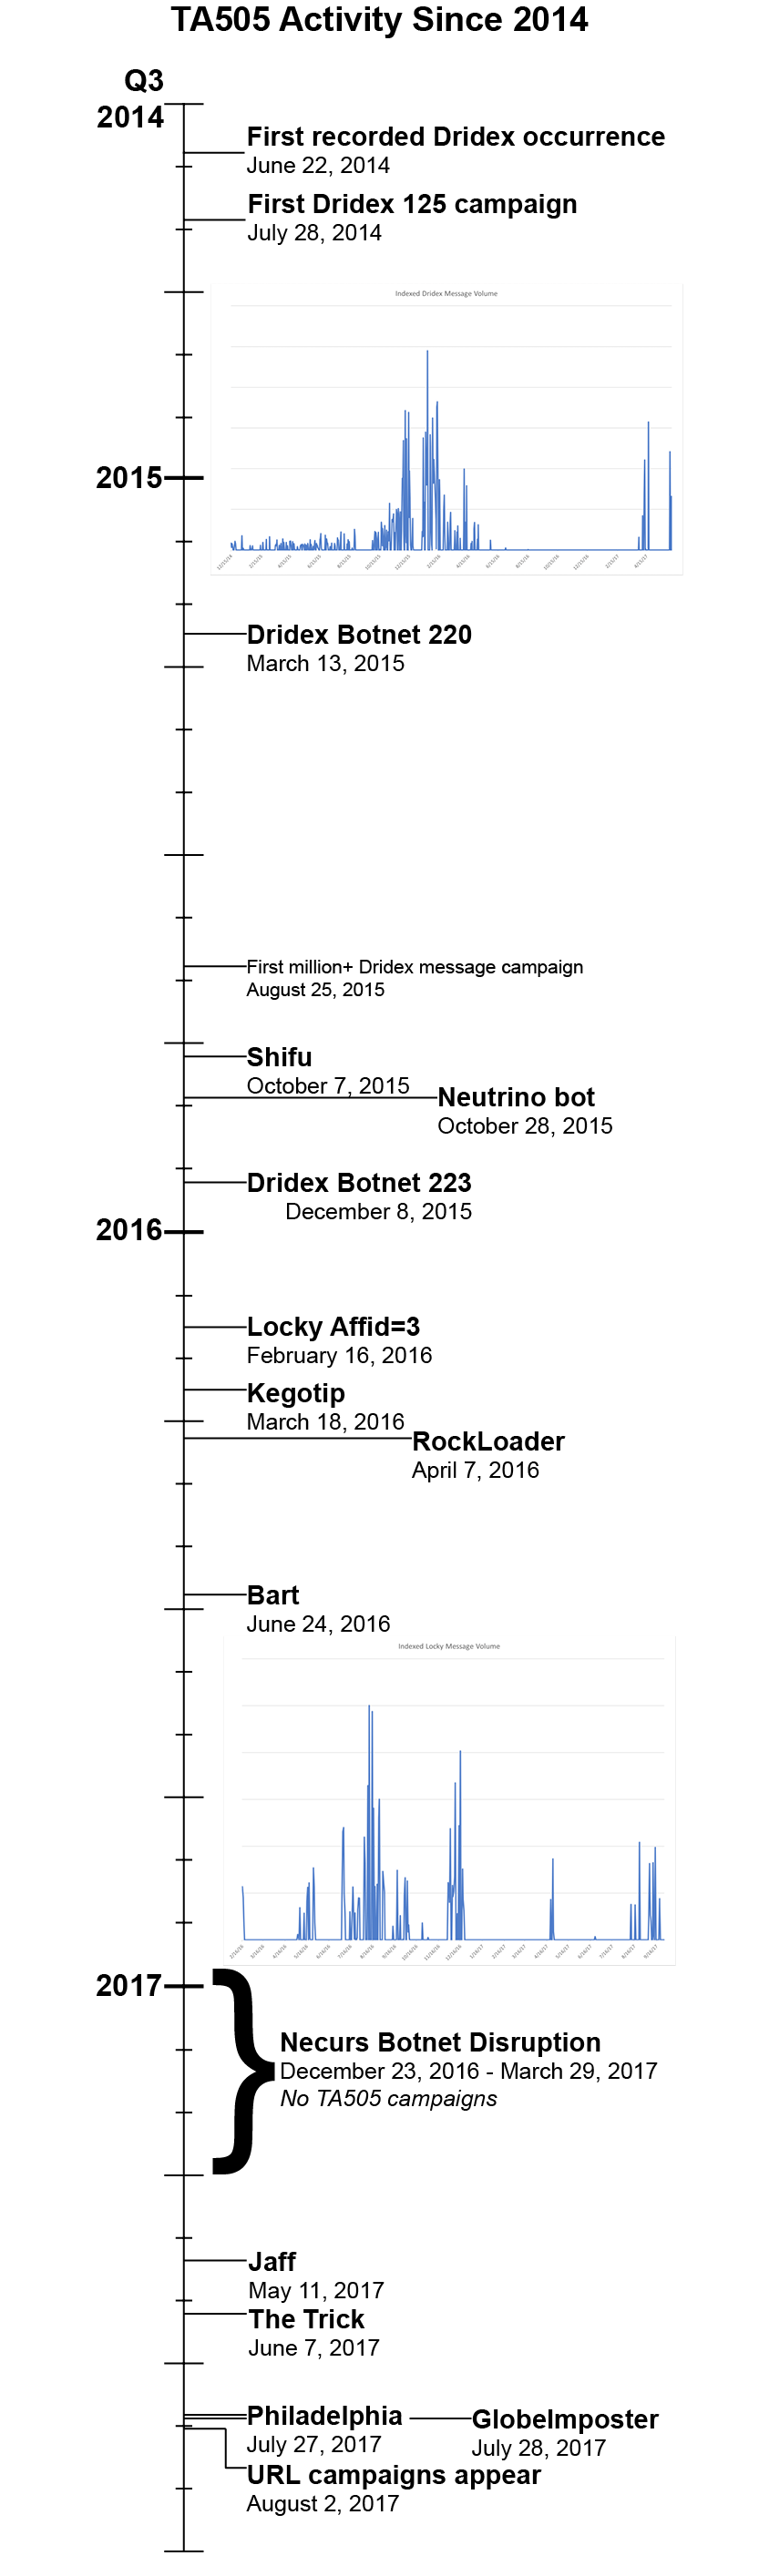
https://www.proofpoint.com/us/threat-insight/post/threat-actor-profile-ta505-dridex-globeimposter
https://threatpost.com/ta505-servhelper-malware/140792/
https://blog.yoroi.company/research/the-stealthy-email-stealer-in-the-ta505-arsenal/
https://threatrecon.nshc.net/2019/08/29/sectorj04-groups-increased-activity-in-2019/
https://www.telekom.com/en/blog/group/article/cybersecurity-ta505-s-box-of-chocolate-597672
https://www.secureworks.com/research/threat-profiles/gold-tahoe
https://blog.fox-it.com/2020/11/16/ta505-a-brief-history-of-their-time/
https://www.secureworks.com/blog/how-cyber-adversaries-are-adapting-to-exploit-the-global-pandemic